Install a browser certificate
6 minute read
The browser and the controller only talk over encrypted connections: HTTPS for the pages and WSS for the live data. Your browser accepts such a connection only when it trusts the controller’s certificate. You make it trust the controller by installing one file, the Motorcortex CA certificateA certificate authority (CA) certificate vouches for other certificates. A browser that trusts a CA accepts every certificate that CA has signed. , once per PC.
Why one file is enough
The controller makes its own server certificate at every start-up, for all of its addresses and its host name, and signs it with the Motorcortex Root CA. Your browser checks that signature. When you have imported the Root CA, the check passes for every controller that uses it, whatever its address.
Download the certificate
Click the button to download mcx.cert.crt. It lands in your downloads folder.

Install it
Where the certificate goes depends on your system and browser. Chrome and Edge on Windows, and Chrome and Safari on macOS, use the certificates of the system. Chrome on Ubuntu has its own list. Firefox has its own list on every system.
Chrome on Ubuntu
Chrome on Ubuntu keeps its own list of trusted certificates. Using Firefox? Open the Firefox tab instead.
-
Type
chrome://certificate-manager/in the address bar and press Enter. -
Go to
Local certificates, and underCustomclickInstalled by you.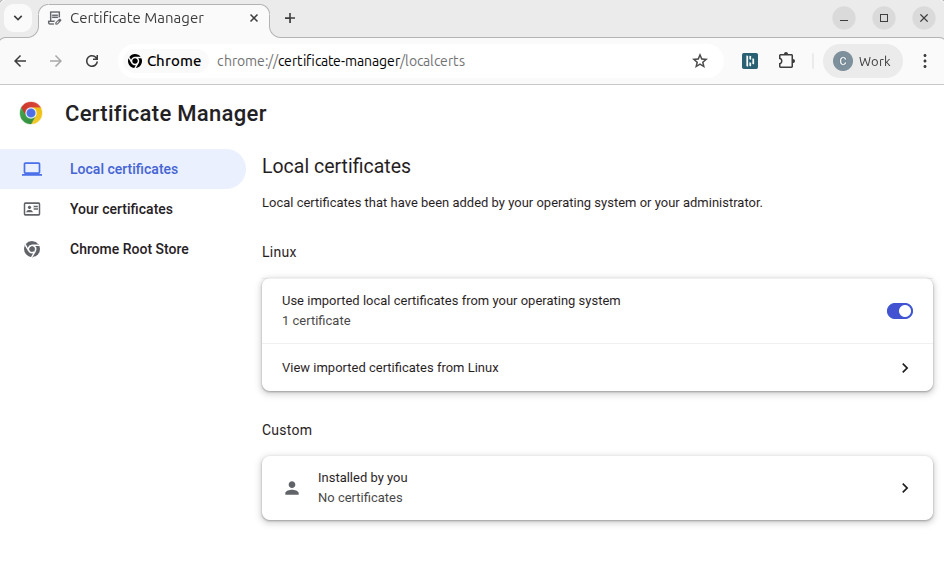
-
Next to
Trusted Certificates, clickImport. -
Select the
mcx.cert.crtyou downloaded and open it. -
Motorcortex Root CAnow shows underTrusted Certificates.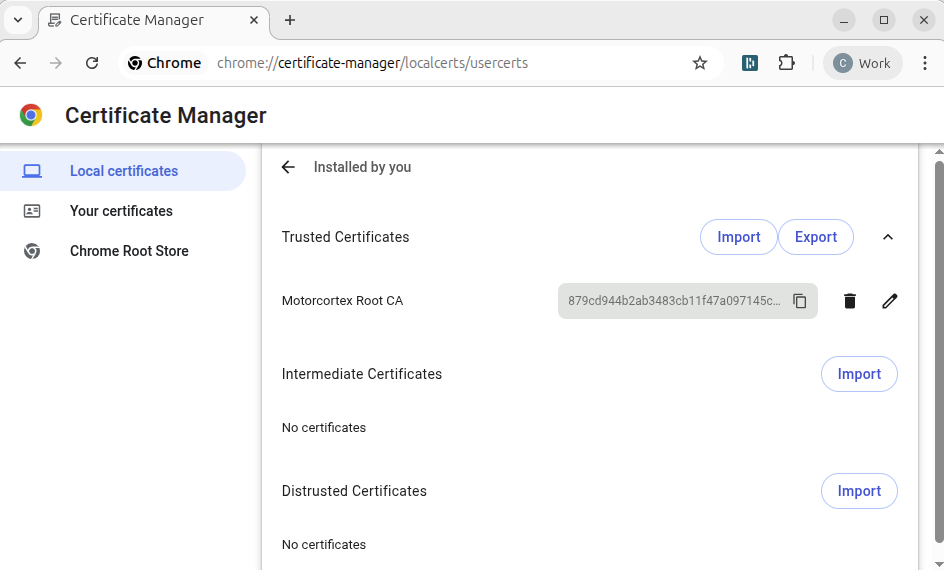
Windows
Chrome and Edge use the certificates of Windows, so you install the file in Windows itself. Using Firefox? Open the Firefox tab instead.
-
Double-click the downloaded
mcx.cert.crt. If Windows asks whether to open it, clickOpen.
-
In the
Certificatewindow, clickInstall Certificate....
-
The
Certificate Import Wizardopens. Keep the store locationCurrent Userand clickNext.
-
Select
Place all certificates in the following store. -
Click
Browse....
-
Select
Trusted Root Certification Authorities. -
Click
OK.
-
Certificate store:now showsTrusted Root Certification Authorities. ClickNext.
-
Click
Finish.
-
Windows warns that you are about to install a root certificate. Click
Yes: this is the certificate you want to trust.
-
Windows reports that the import was successful. Click
OK.
-
Restart Windows, so every browser picks up the certificate.
macOS
Chrome and Safari use the certificates in Keychain Access, so you install the file there. Using Firefox? Open the Firefox tab instead.
-
Double-click the downloaded
mcx.cert.crtand allowKeychain Accessto add it.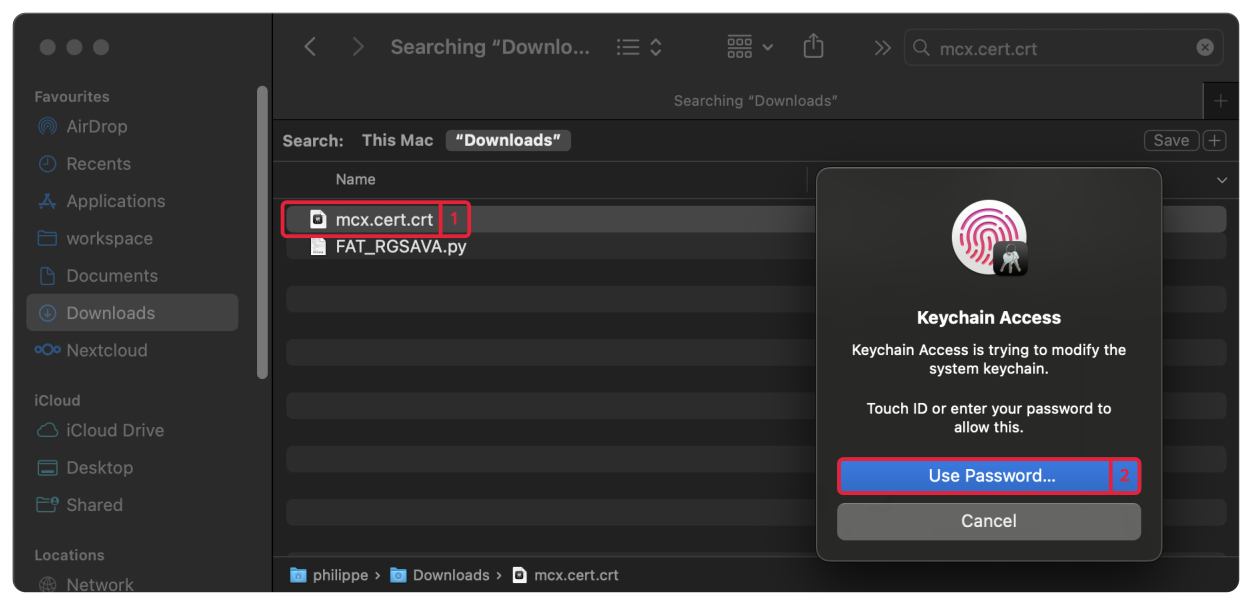
-
Motorcortex Root CAnow shows inKeychain Access, but it is not trusted yet.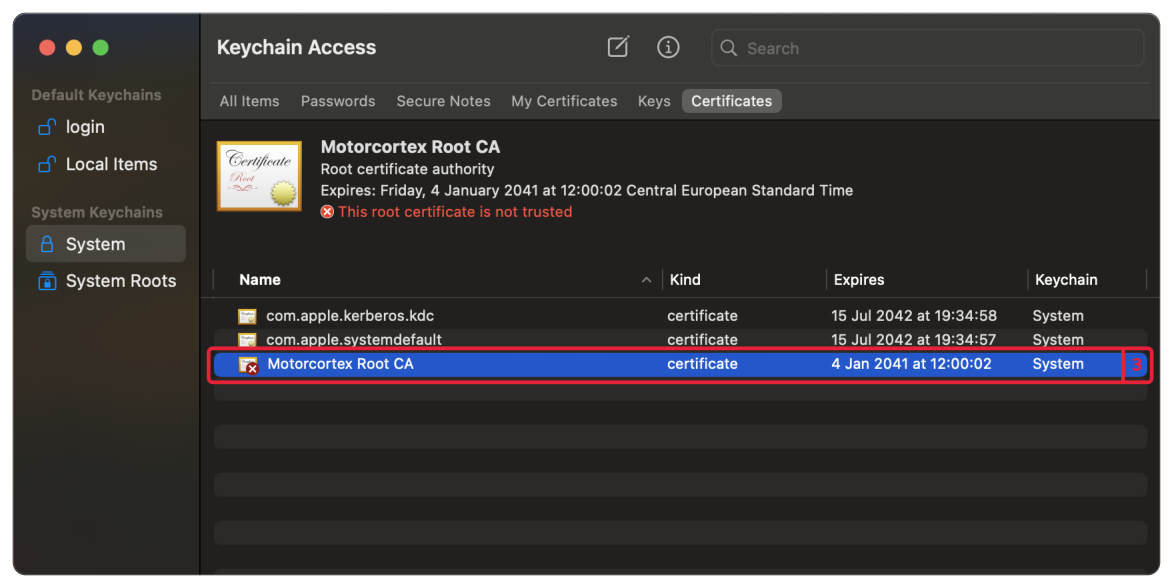
-
Double-click
Motorcortex Root CAto open its trust settings. -
Set
When using this certificatetoAlways Trust.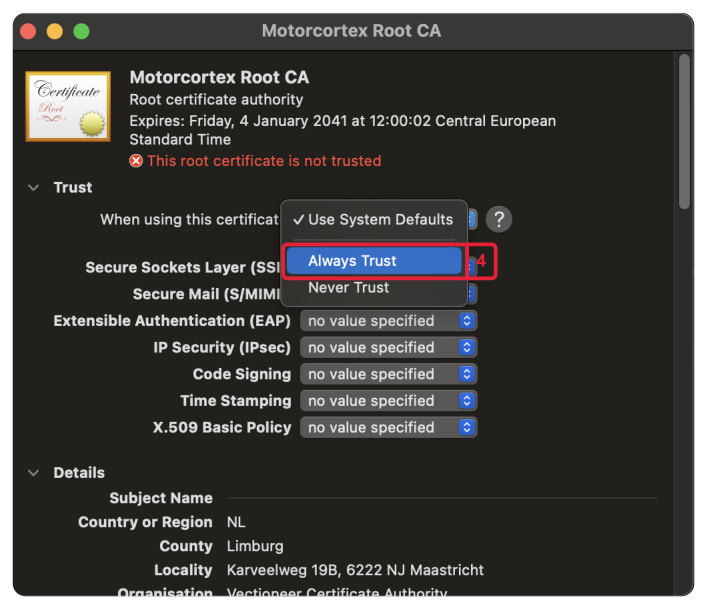
-
Close the window and confirm with your macOS password to save the change.
Firefox
Firefox keeps its own list of trusted certificates, so you import the file in Firefox itself. The steps are the same on every system.
-
Open the menu at the top right.
-
Open
Settings.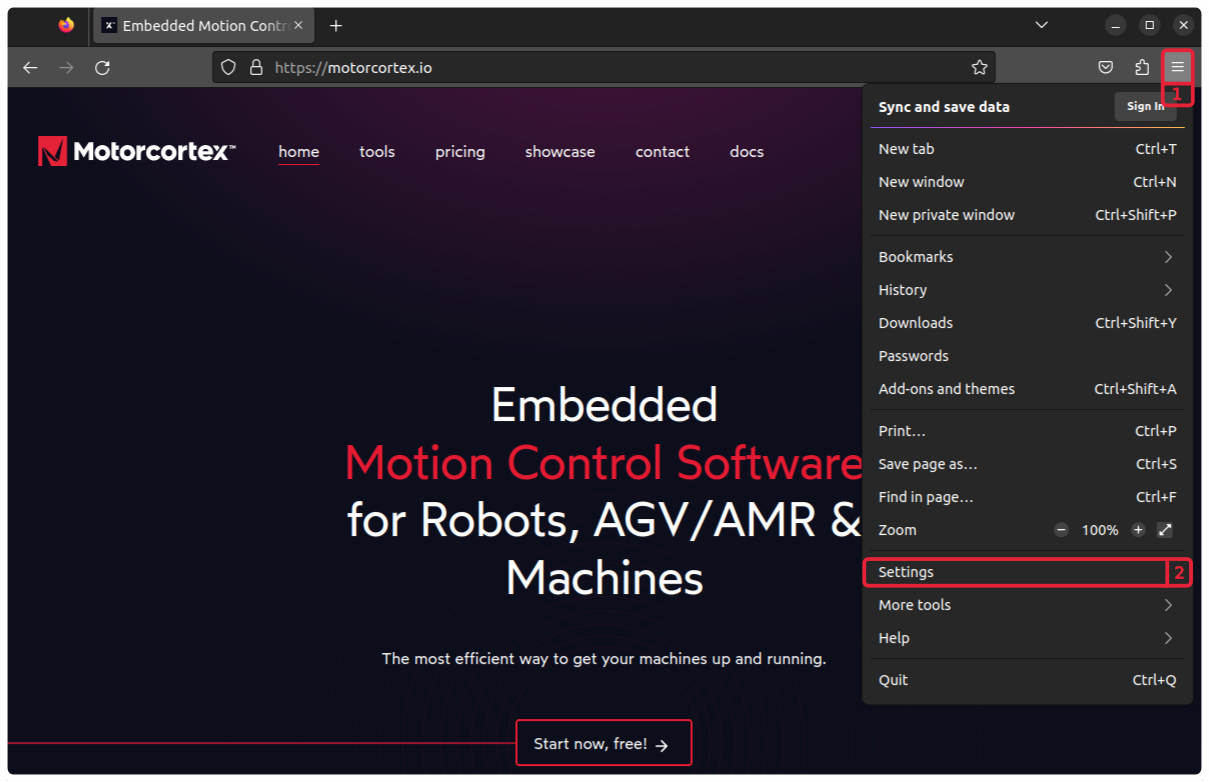
-
Go to
Privacy & Security. -
Scroll down to
Securityand clickView Certificates....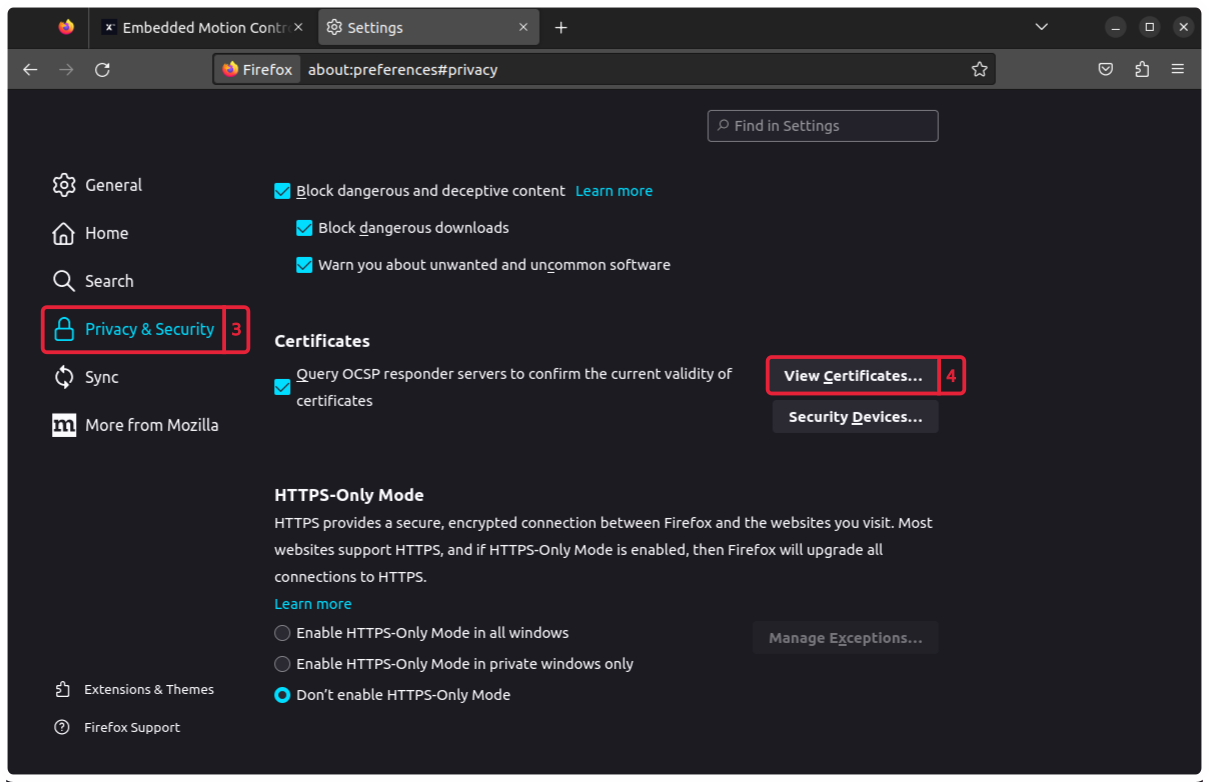
-
In the
Certificate Manager, open theAuthoritiestab. -
Click
Import....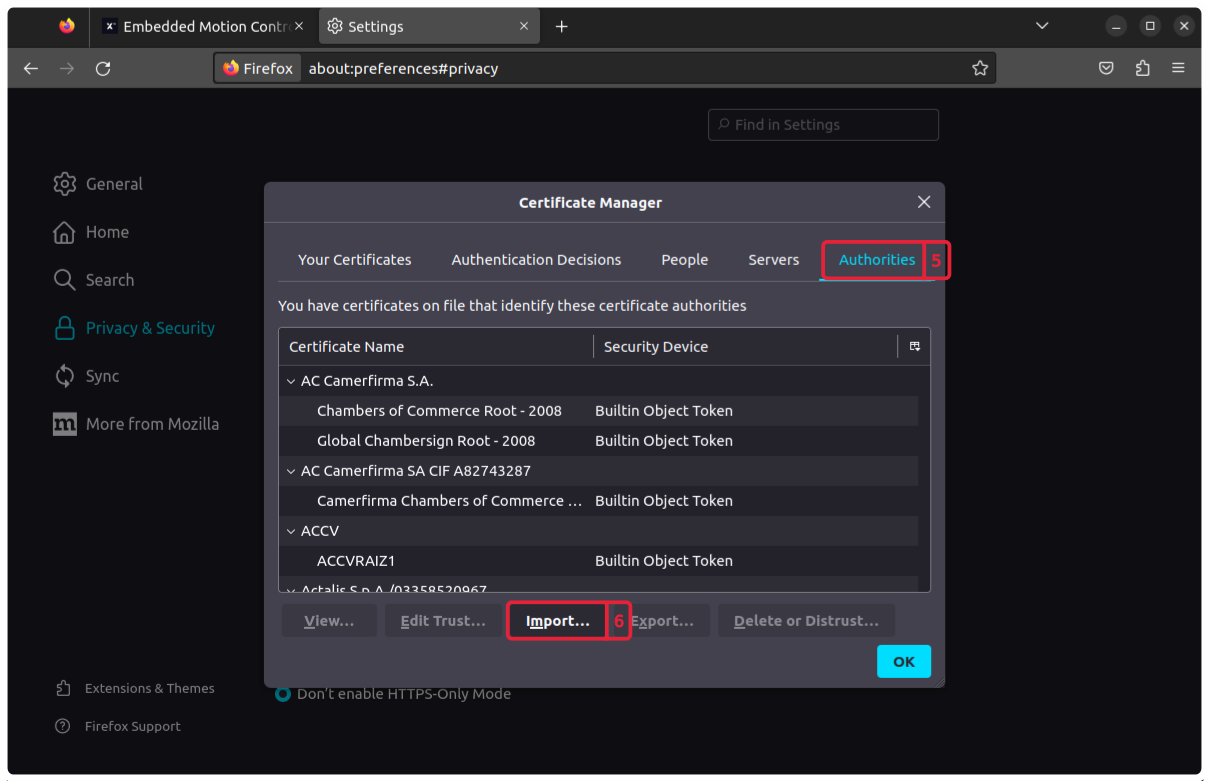
-
Select the
mcx.cert.crtyou downloaded and open it. -
In the
Downloading Certificatewindow, tickTrust this CA to identify websites. -
Click
OK.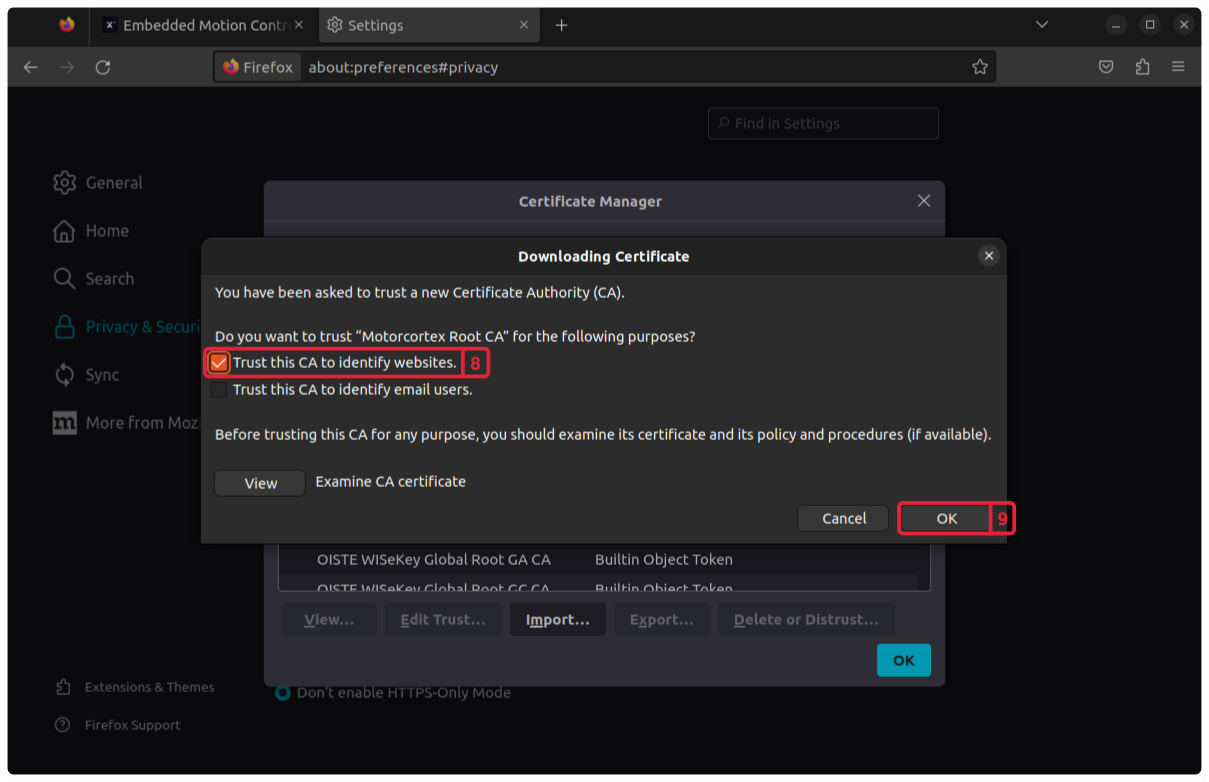
Check it works
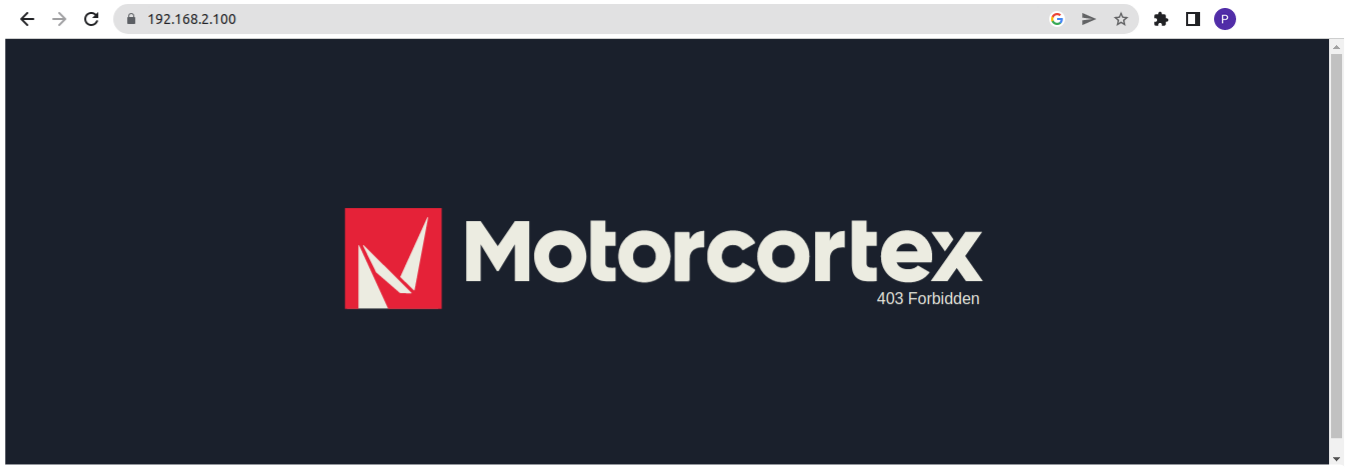
Open https://controller_ip_addressThe IP address of your controller. In most cases 192.168.2.100. in the browser you installed the certificate for.
It works
The address bar shows a padlock and the Motorcortex page opens. The text under the logo does not matter here; the padlock does.
It does not work
Chrome shows Your connection is not private with the code NET::ERR_CERT_AUTHORITY_INVALID. Chrome does not trust the certificate yet.
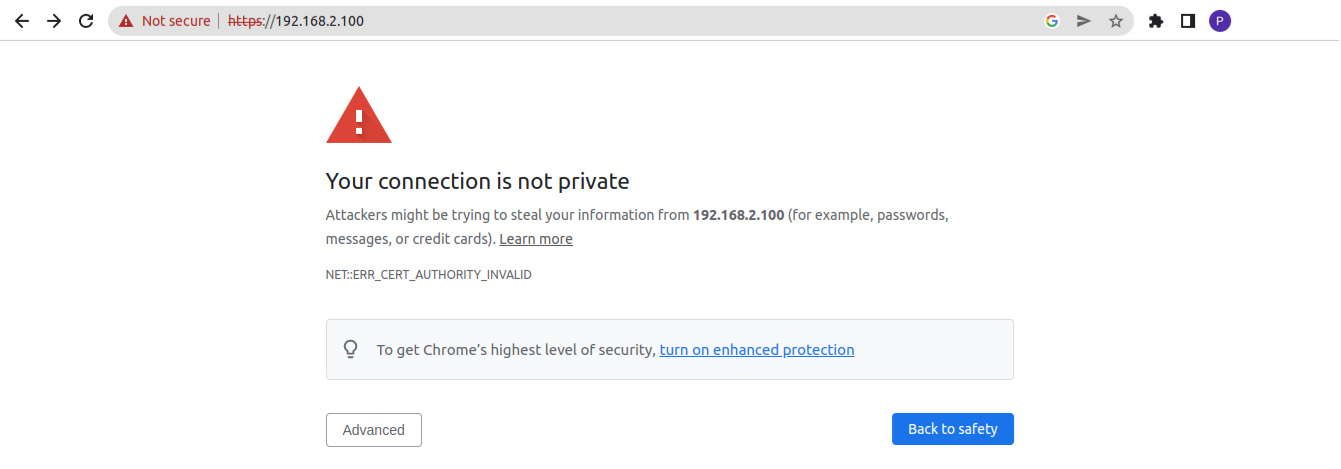
Check that Motorcortex Root CA is in the list where you imported it: under Installed by you in chrome://certificate-manager/ on Ubuntu, in the Windows store, or in Keychain Access with Always Trust on macOS. If it is missing, install it again.
It works
The address bar shows a padlock and the Motorcortex page opens. The text under the logo does not matter here; the padlock does.
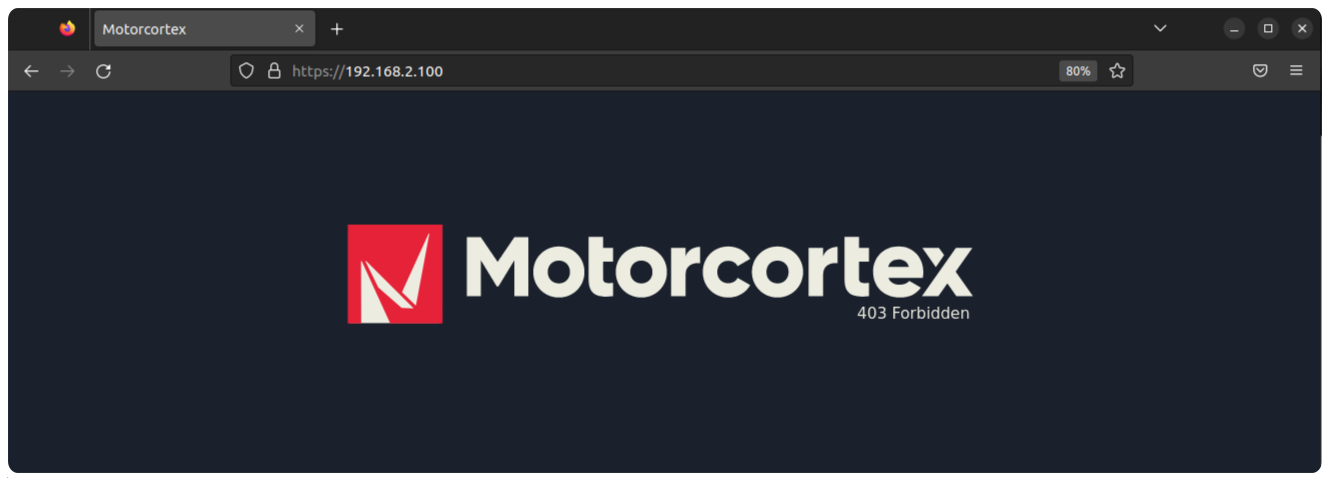
It does not work
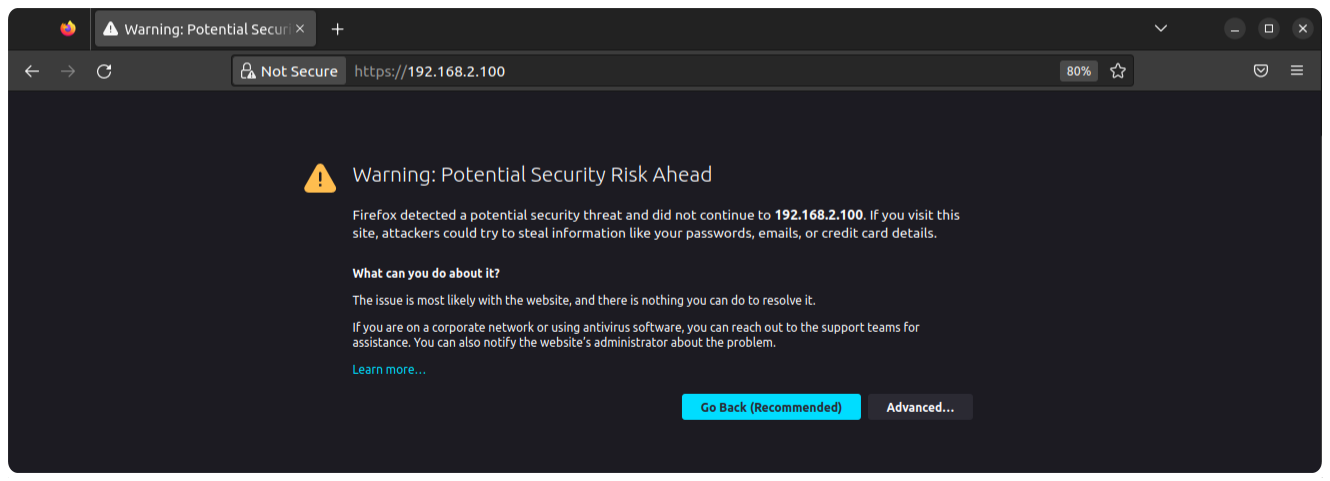
Firefox shows Warning: Potential Security Risk Ahead. Firefox does not trust the certificate yet.
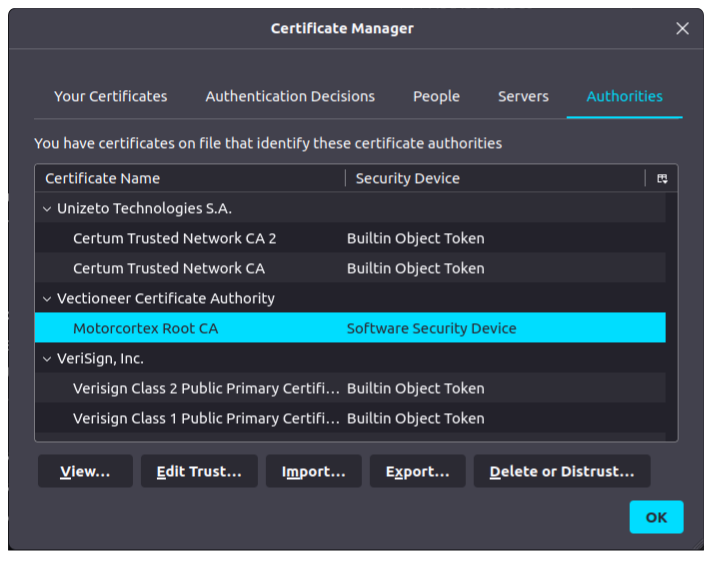
Check that the certificate is in the Authorities tab of the Firefox Certificate Manager: look for Motorcortex Root CA under Vectioneer Certificate Authority. If it is missing, import it again.
Still a warning after a new import? Close every window of the browser and open it again. For other browser problems, see the FAQ.